DigiCert Discloses a Data Breach After a Server Migration Error
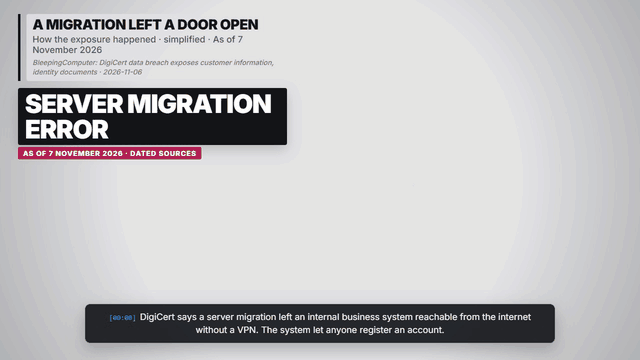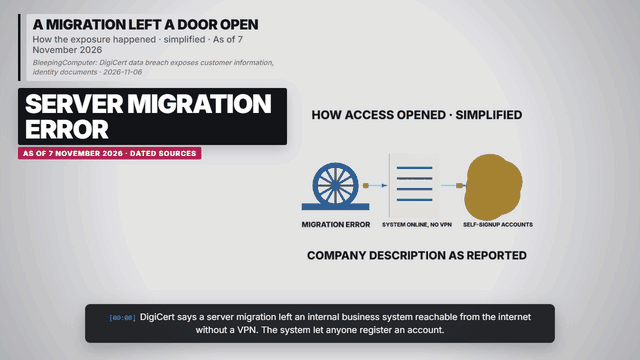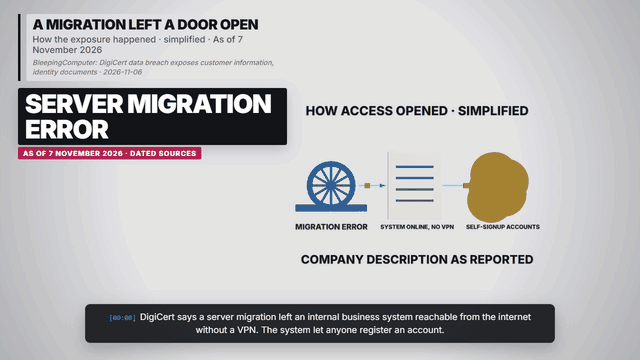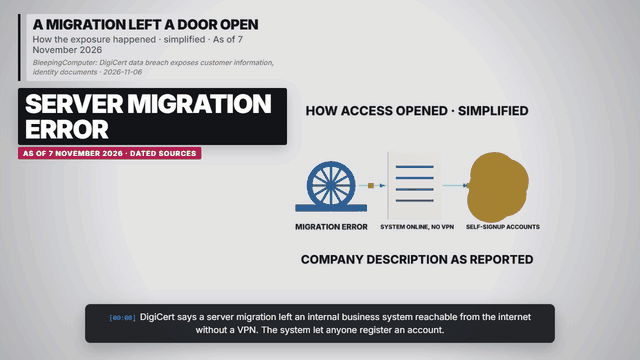
DigiCert says a server-migration error left an internal system reachable online, letting outsiders read archived customer data, including some ID documents, in June–July 2026. Certificate services were not affected.
Explore the six-scene explainerKey takeaways
- DigiCert says a server-migration error exposed an internal system without a VPN, and outsiders could register accounts.
- The accounts could read archived customer data between 27 June and 2 July 2026; some records included IDs.
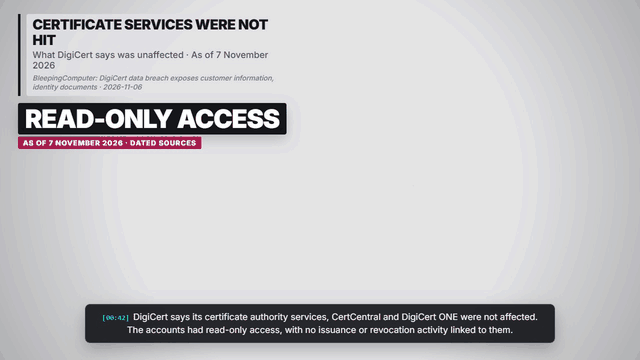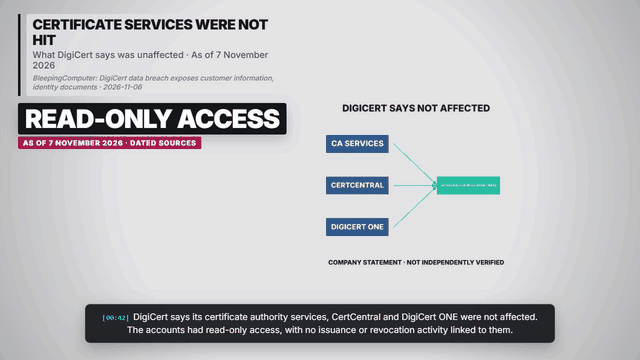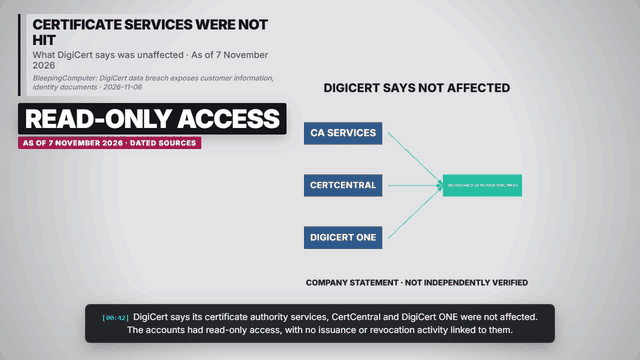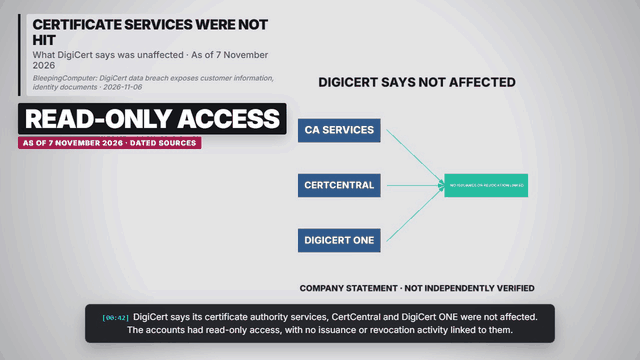
- DigiCert says certificate services, CertCentral and DigiCert ONE were not affected.
Sourced figures and status
| Period | Figure or status | Source |
|---|---|---|
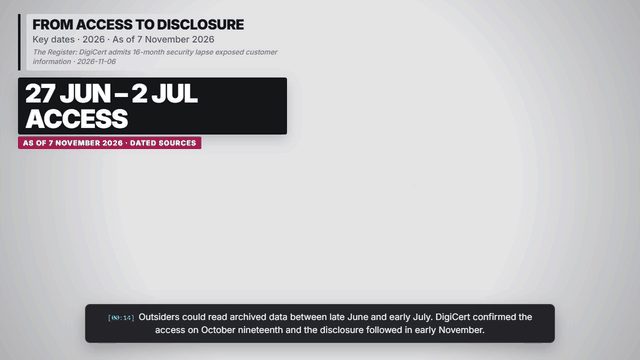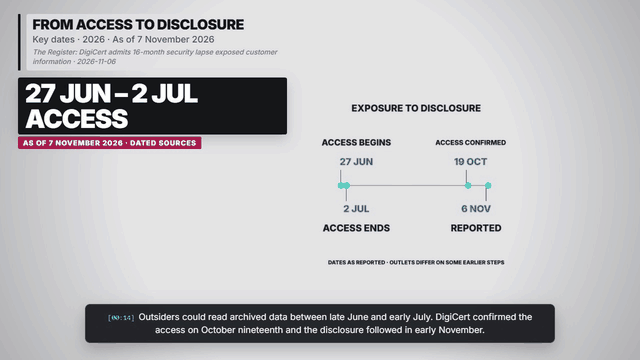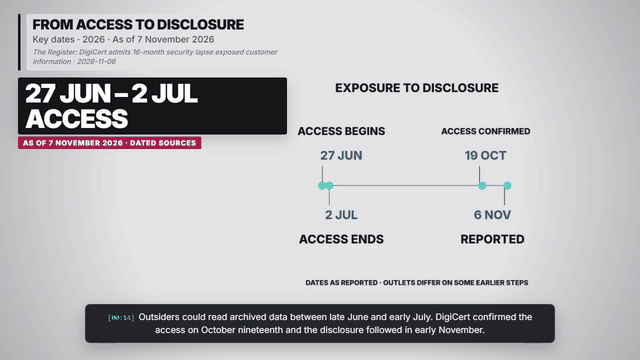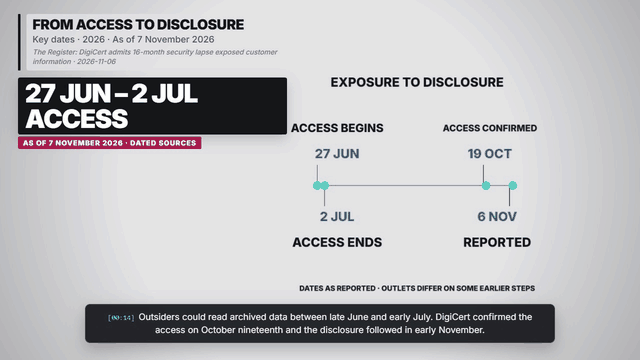
| 27 Jun – 2 Jul 2026 | Unauthorized accounts read archived customer data (read-only). | BleepingComputer: DigiCert data breach exposes customer information, identity documents · 2026-11-06 |
| 19 Oct 2026 | Access confirmed after a later investigation. | The Register: DigiCert admits 16-month security lapse exposed customer information · 2026-11-06 |
| 6 Nov 2026 | Breach reported by security outlets. | The Register: DigiCert admits 16-month security lapse exposed customer information · 2026-11-06 |
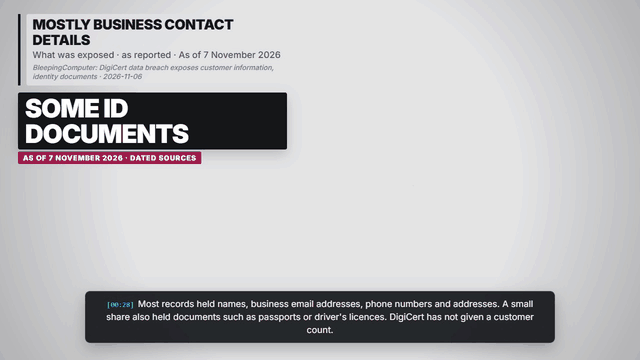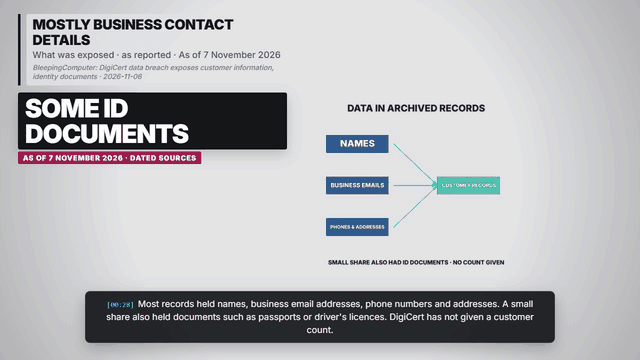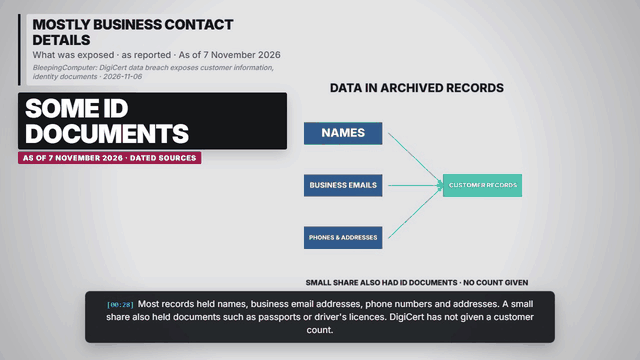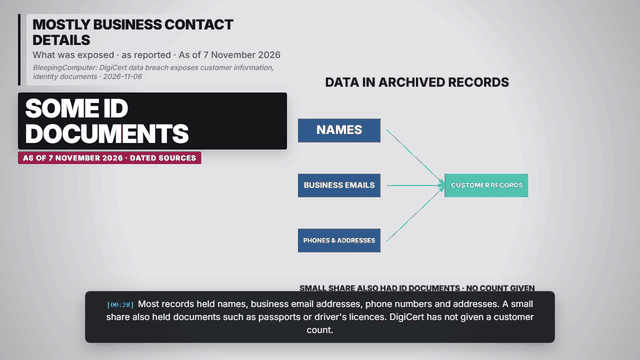
| Data | Names, business emails, phones, addresses; a small share also ID documents. | SC Media: DigiCert reports data breach following server migration error · 2026-11-06 |
| Scope | CA services, CertCentral, DigiCert ONE stated unaffected; no customer count published. | SC Media: DigiCert reports data breach following server migration error · 2026-11-06 |
What is a self-registration flaw?
It means a system let any visitor create an account. Combined with weak authorization, those accounts could view data they should not have seen. Source and context.
Does this affect website certificates?
DigiCert says no: its CA services were not affected and no issuance or revocation activity was linked to the accounts. This is the company's statement. Source and context.
Charts, maps and diagrams from the explainer
Frequently asked questions
What happened at DigiCert?
A server-migration error left an internal system reachable online, and outsiders could read archived customer data.
Were IDs exposed?
DigiCert says a small share of records included documents such as passports or driver's licences.
Were certificate services affected?
DigiCert says CA services, CertCentral and DigiCert ONE were not affected.
Sources and reporting scope
BleepingComputer: DigiCert data breach exposes customer information, identity documents. 2026-11-06. Server-migration error exposed an internal business system; outsiders could self-register and read archived customer data; some records include IDs.
The Register: DigiCert admits 16-month security lapse exposed customer information. 2026-11-06. Timeline of exposure and detection; says the full report was filed with Mozilla's CA compliance tracker.
SC Media: DigiCert reports data breach following server migration error. 2026-11-06. Summary of affected data types and unaffected services.
As of 7 November 2026. The account is DigiCert's own disclosure as reported by security outlets; DigiCert has not published a customer count. Outlets differ on some dates, including when the migration took place and when investigation steps began. Certificate-issuance services are stated to be unaffected. Re-check against DigiCert's incident report before re-rendering.