A leaked vendor key let attackers plant a fake extension in Cursor
Cursor said on 13 November 2026 that an access key exposed by its inference vendor Fireworks AI let attackers plant tampered Claude Code extension builds in its marketplace on 29 October, reaching up to about 5,000 users.
Explore the six-scene explainerKey takeaways
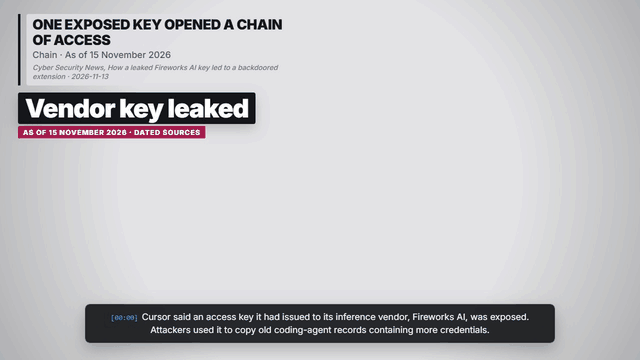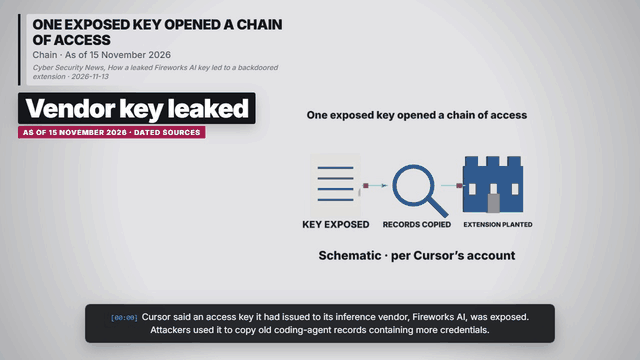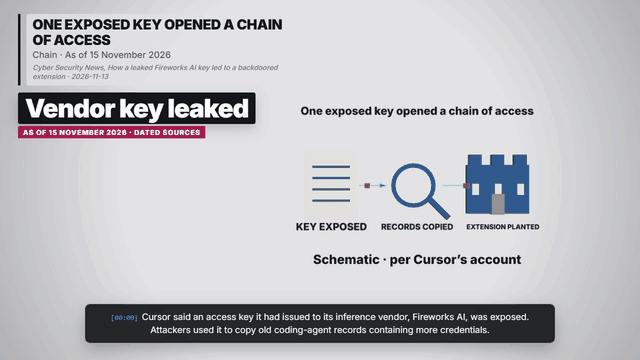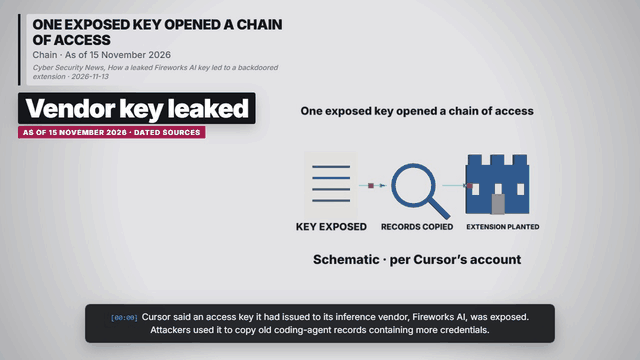
- An access key Cursor had issued to its inference vendor Fireworks AI was exposed. It gave read access to a shared storage bucket, from which the attacker copied historical coding-agent records containing further credentials.
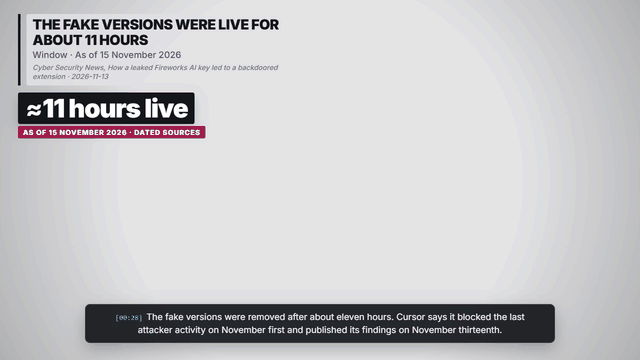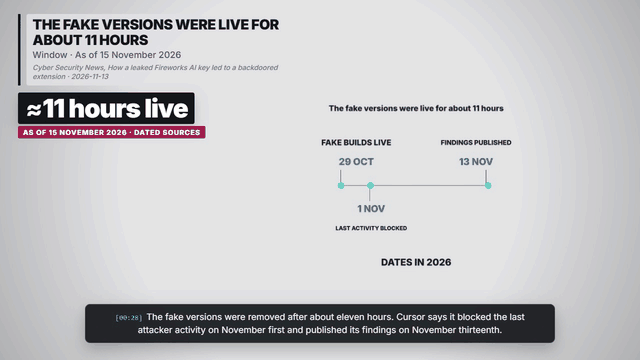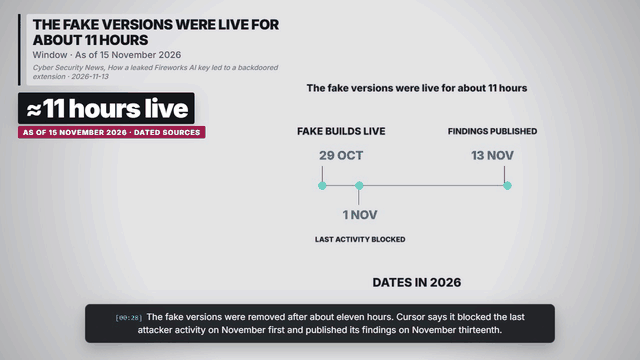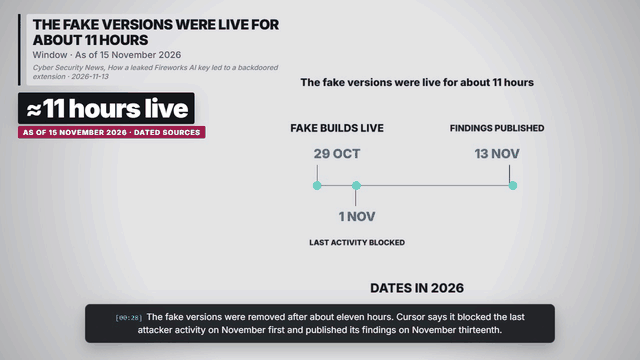
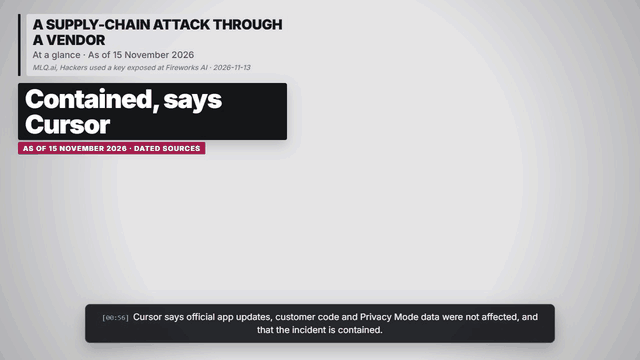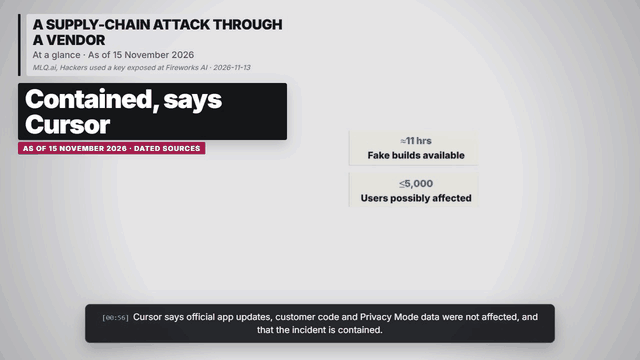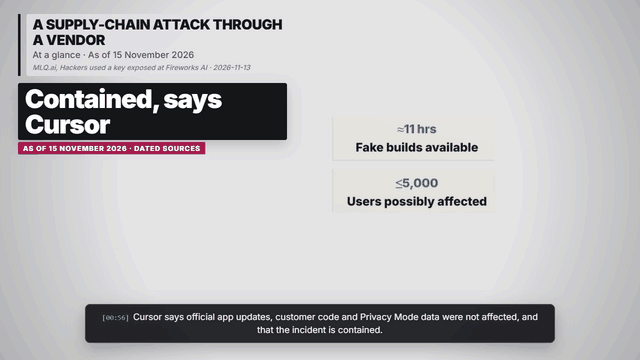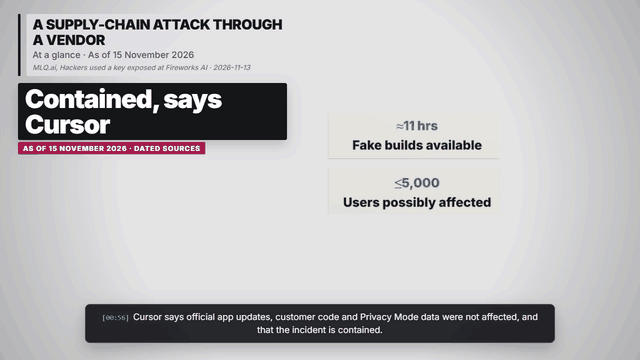
- Tampered builds of the Claude Code extension, versions 2.1.312 and 2.1.313 for Windows and macOS, were placed in the cache serving Cursor’s marketplace and removed after about 11 hours.
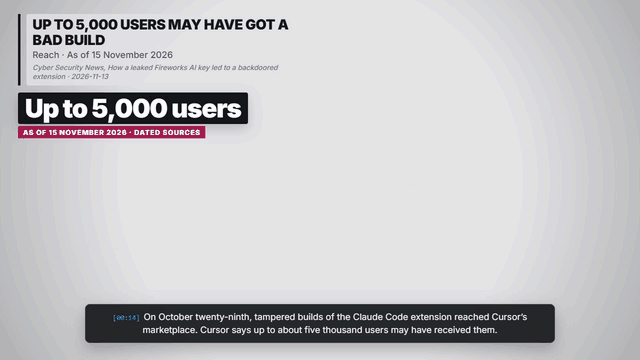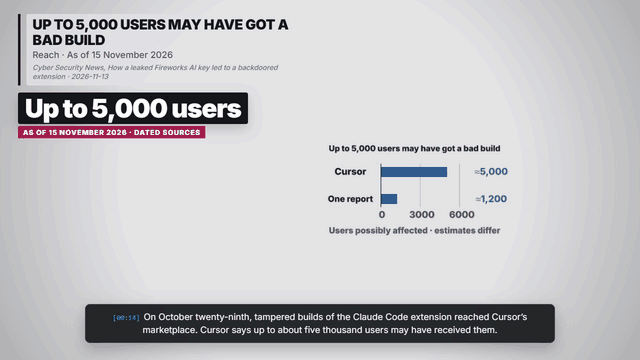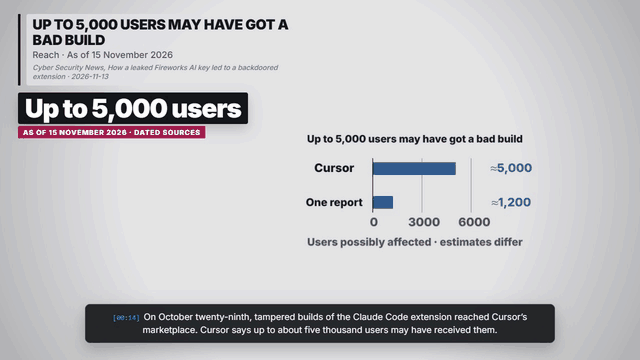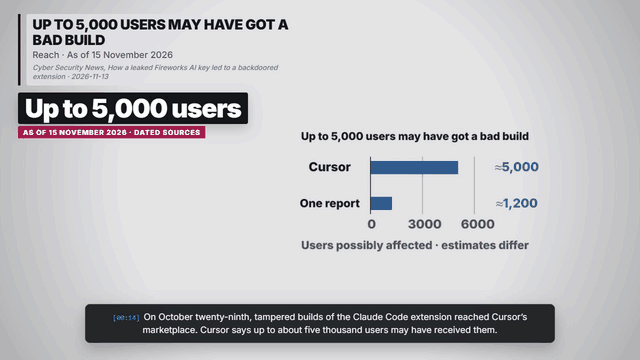
- Cursor says up to about 5,000 users may have received a tampered build; one outlet reported about 1,200 installations.
Sourced figures and status
| Period | Figure or status | Source |
|---|---|---|
| Entry point | An access key Cursor had issued to its inference vendor Fireworks AI was exposed. It gave read access to a shared storage bucket, from which the attacker copied historical coding-agent records containing further credentials. | Cyber Security News, How a leaked Fireworks AI key led to a backdoored extension · 2026-11-13 |
| 29 October | Tampered builds of the Claude Code extension, versions 2.1.312 and 2.1.313 for Windows and macOS, were placed in the cache serving Cursor’s marketplace and removed after about 11 hours. | Cyber Security News, How a leaked Fireworks AI key led to a backdoored extension · 2026-11-13 |
| Users | Cursor says up to about 5,000 users may have received a tampered build; one outlet reported about 1,200 installations. | Cyber Security News, How a leaked Fireworks AI key led to a backdoored extension · 2026-11-13 |
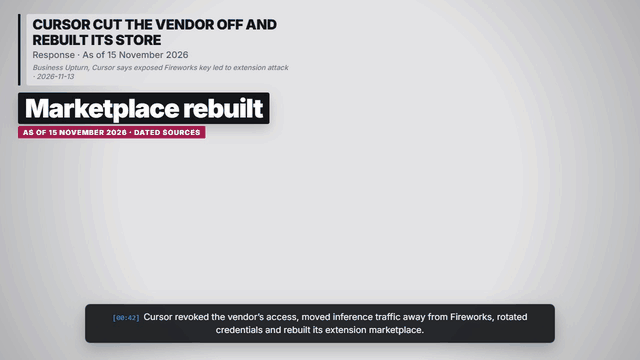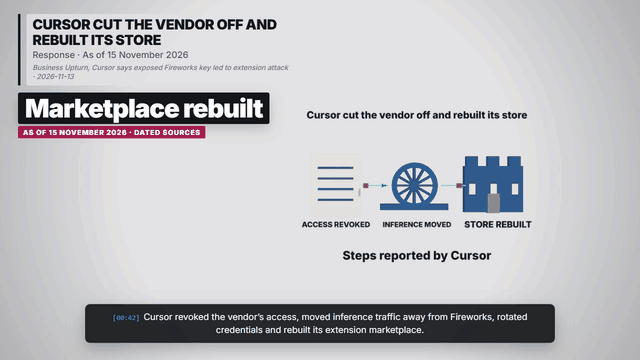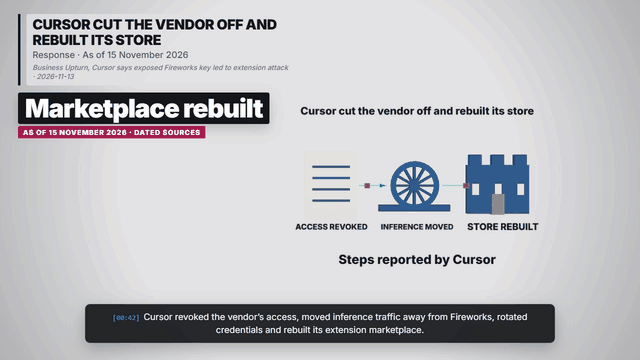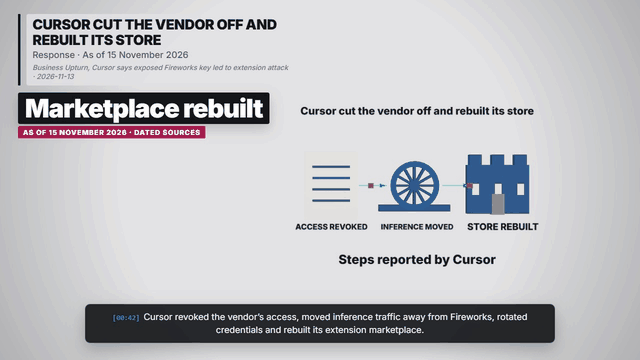
| Response | Cursor revoked the vendor’s access, moved inference traffic away from Fireworks, rotated internal credentials and rebuilt the extension marketplace. It says it blocked the last attacker activity on 1 November. | Business Upturn, Cursor says exposed Fireworks key led to extension attack · 2026-11-13 |
What was not affected
Cursor says official app releases, customer code repositories and Privacy Mode data were not affected. The hidden code collected host and user details and tried to install a persistent remote-access backdoor. Source and context.
What is still unknown
Fireworks has not published a detailed account of how the key was exposed, and outside counts of affected users differ from Cursor’s estimate. Source and context.
Charts, maps and diagrams from the explainer
Frequently asked questions
How did attackers get into Cursor’s marketplace?
An access key Cursor had issued to its inference vendor Fireworks AI was exposed. It gave read access to a shared storage bucket, from which the attacker copied historical coding-agent records containing further credentials.
How many Cursor users were affected?
Cursor says up to about 5,000 users may have received a tampered build; one outlet reported about 1,200 installations.
Sources and reporting scope
Cyber Security News, How a leaked Fireworks AI key led to a backdoored extension. 2026-11-13. Summary of Cursor’s 13 November investigation update: entry point, tampered versions, user count and exposure window. In English.
Business Upturn, Cursor says exposed Fireworks key led to extension attack. 2026-11-13. Cursor’s response: vendor access revoked, inference moved, credentials rotated and marketplace rebuilt. In English.
MLQ.ai, Hackers used a key exposed at Fireworks AI. 2026-11-13. What the hidden code did and what Cursor says was not affected. In English.
DEV Community, Cursor’s security incident explained. 2026-11-14. Developer explainer on the attack chain; secondary analysis of Cursor’s report. In English.
As of 15 November 2026. Figures come from Cursor’s investigation update as reported by the outlets listed; the user count is Cursor’s upper estimate and other reports differ. Fireworks has not published a detailed account. The attack chain is schematic.