Full transcript
The narration below matches the explainer. Its original reporting dates and qualifications still apply.
One exposed key opened a chain of access
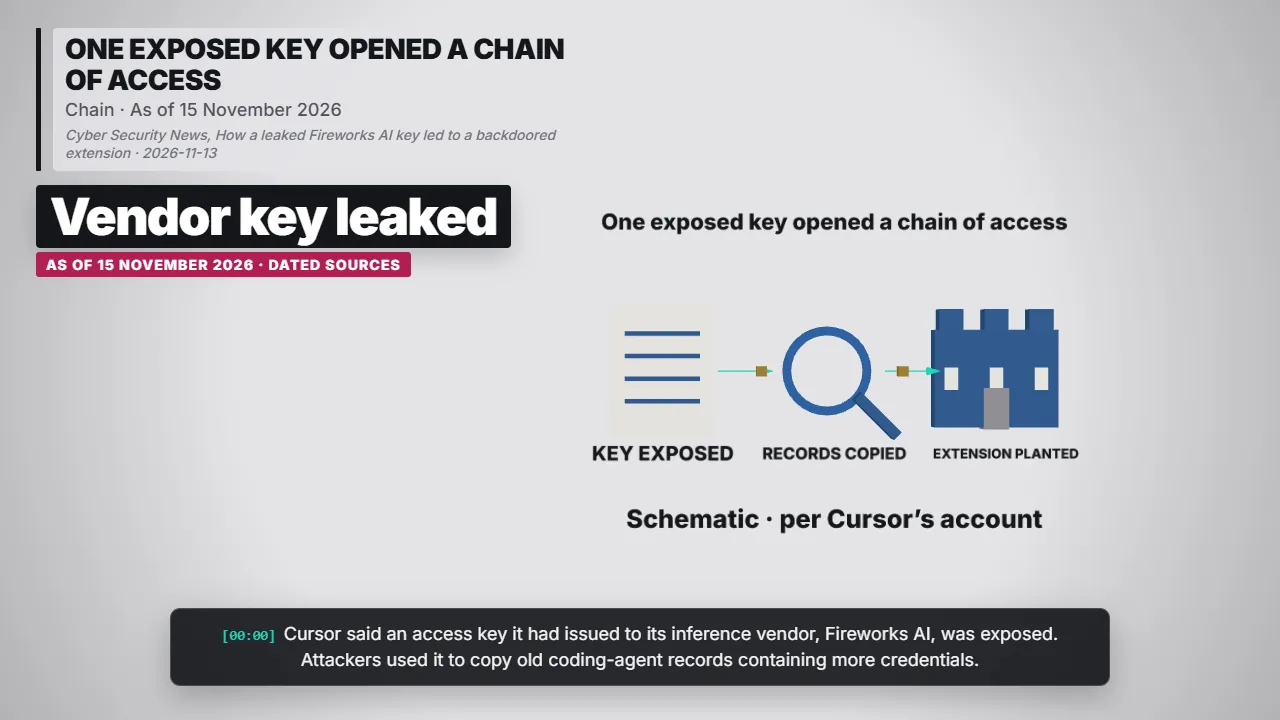
Cursor said an access key it had issued to its inference vendor, Fireworks AI, was exposed. Attackers used it to copy old coding-agent records containing more credentials.
Cyber Security News, How a leaked Fireworks AI key led to a backdoored extension · 2026-11-13
Up to 5,000 users may have got a bad build
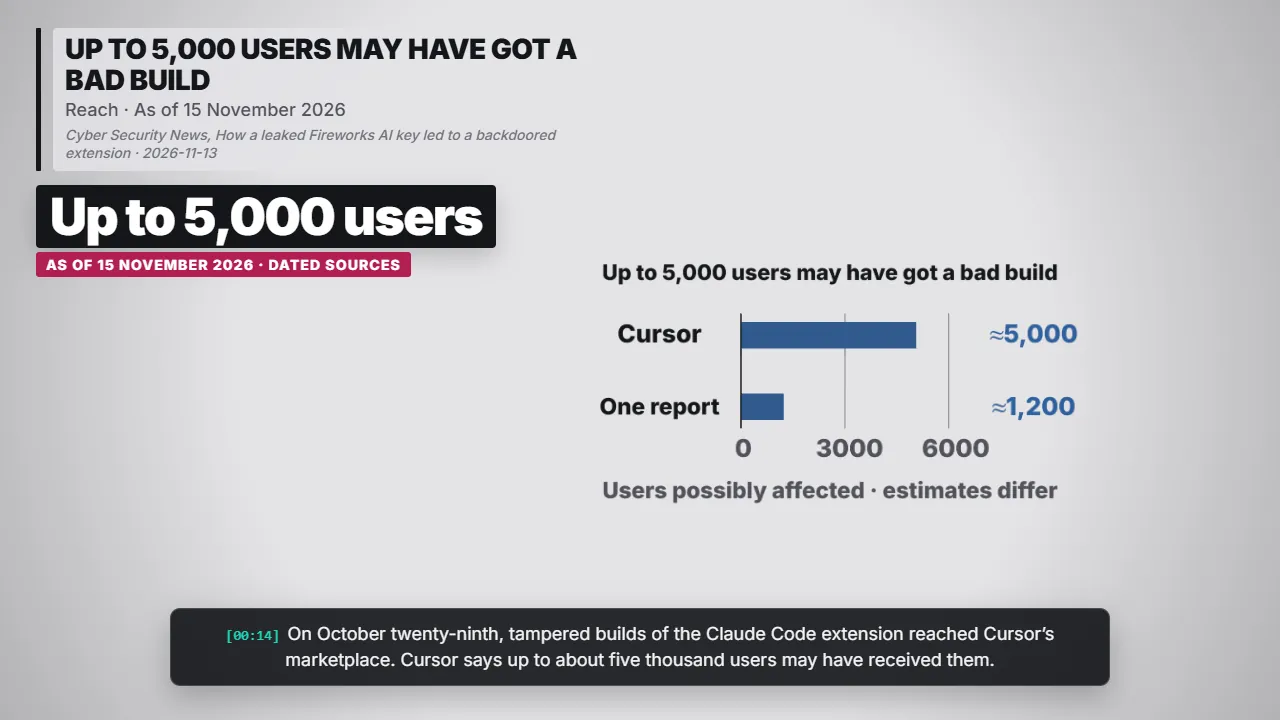
On October twenty-ninth, tampered builds of the Claude Code extension reached Cursor’s marketplace. Cursor says up to about five thousand users may have received them.
Cyber Security News, How a leaked Fireworks AI key led to a backdoored extension · 2026-11-13
The fake versions were live for about 11 hours
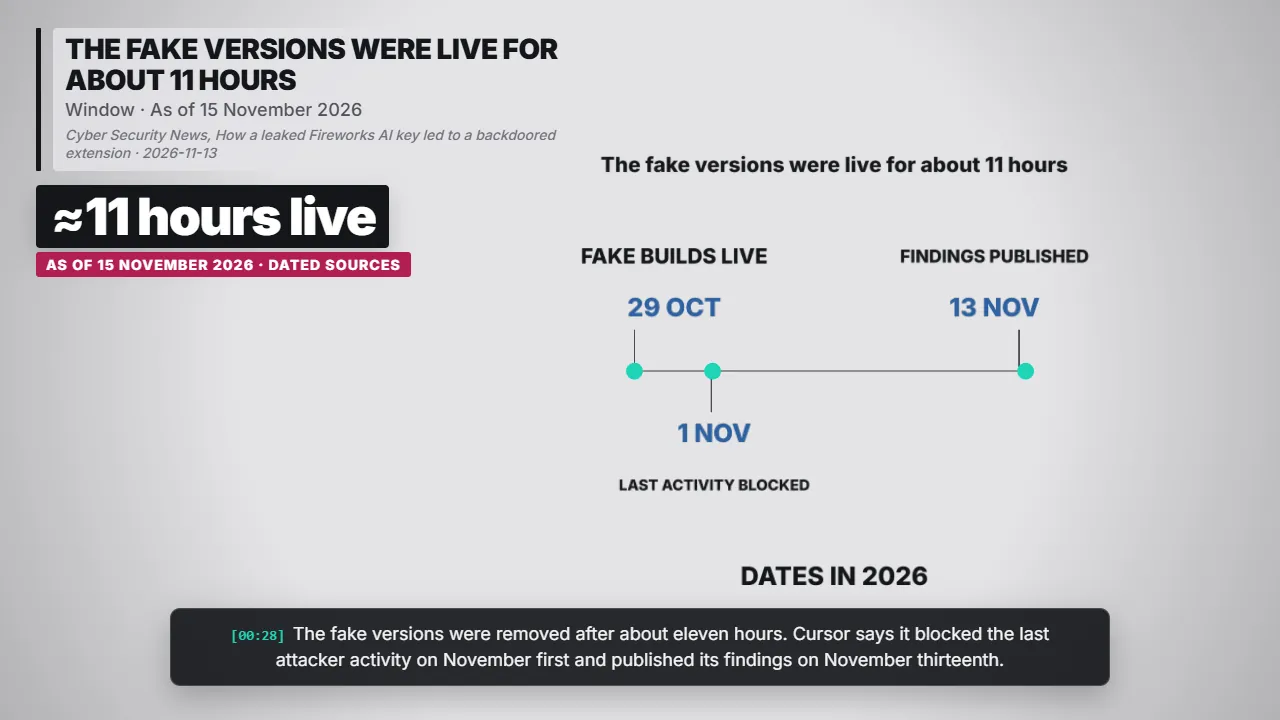
The fake versions were removed after about eleven hours. Cursor says it blocked the last attacker activity on November first and published its findings on November thirteenth.
Cyber Security News, How a leaked Fireworks AI key led to a backdoored extension · 2026-11-13
Cursor cut the vendor off and rebuilt its store
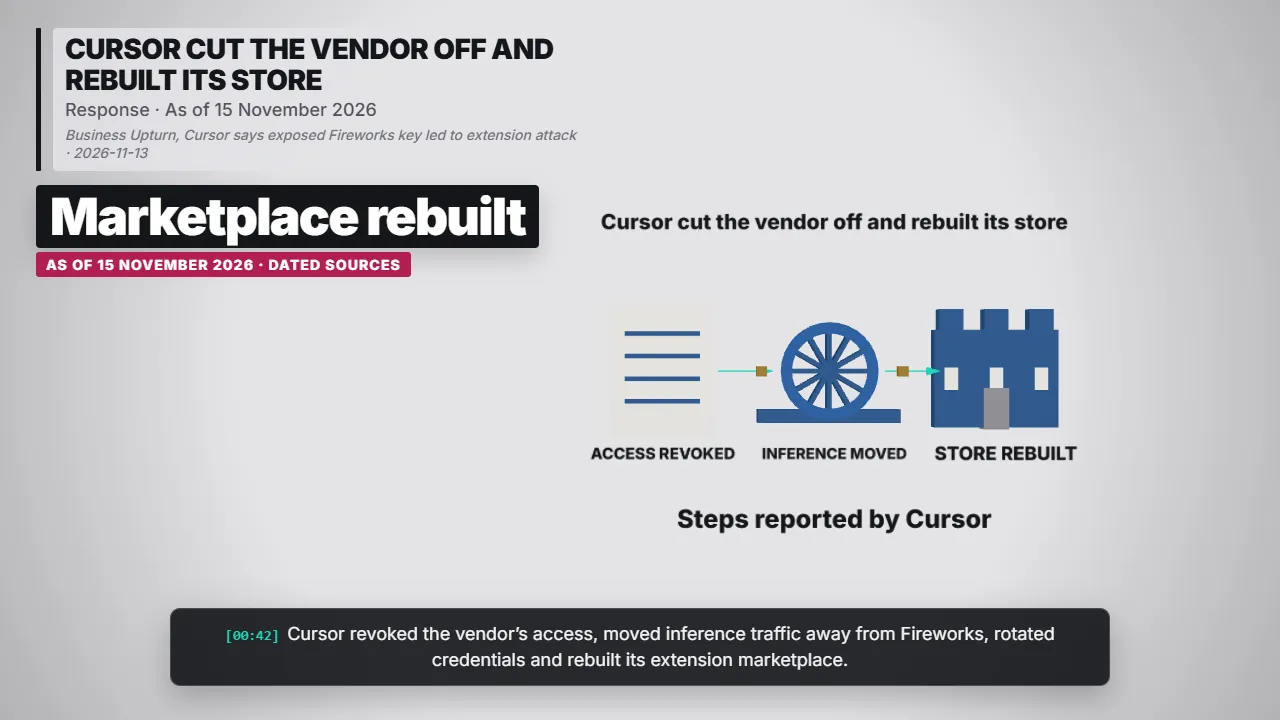
Cursor revoked the vendor’s access, moved inference traffic away from Fireworks, rotated credentials and rebuilt its extension marketplace.
Business Upturn, Cursor says exposed Fireworks key led to extension attack · 2026-11-13
A supply-chain attack through a vendor
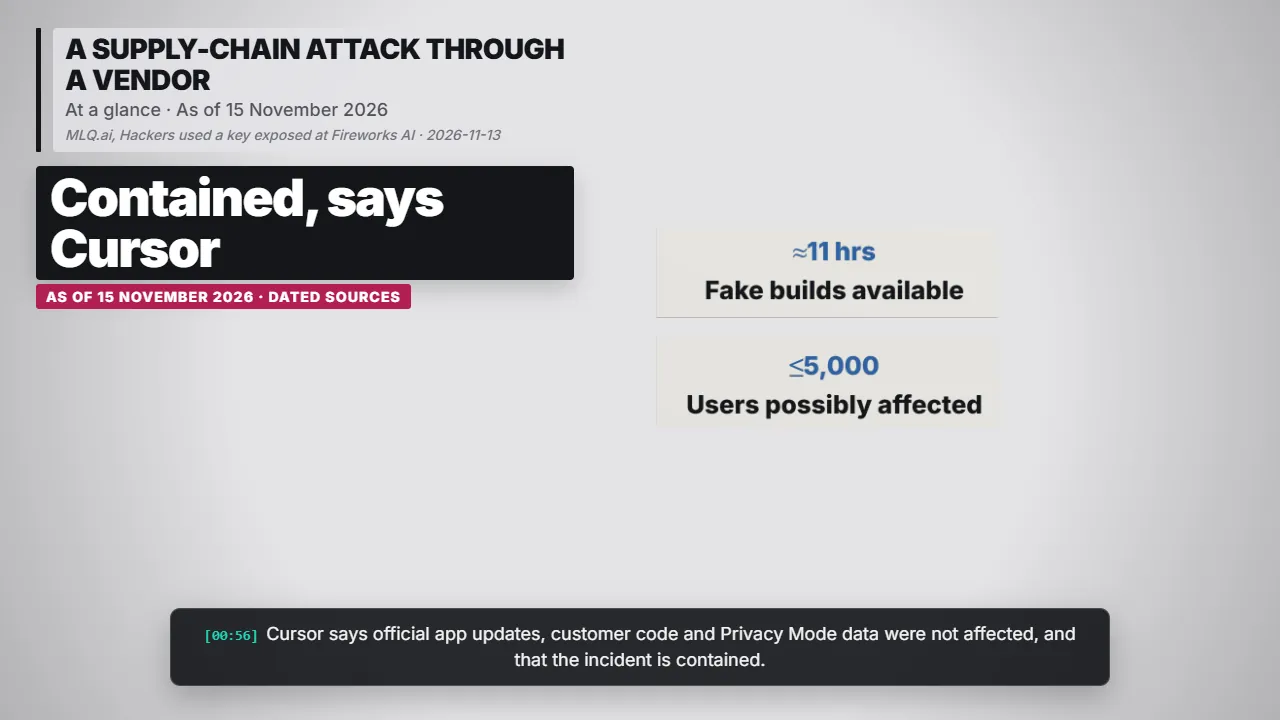
Cursor says official app updates, customer code and Privacy Mode data were not affected, and that the incident is contained.
MLQ.ai, Hackers used a key exposed at Fireworks AI · 2026-11-13
SOURCES AND NOTES
Cyber Security News, Business Upturn and MLQ dot A I summarised Cursor’s update. A DEV Community post explained the attack chain.
Cyber Security News, How a leaked Fireworks AI key led to a backdoored extension · 2026-11-13
Source links
- https://cybersecuritynews.com/cursor-data-breach/
- https://businessupturn.com/technology/cursor-says-exposed-fireworks-access-key-led-to-claude-code-extension-attack/
- https://mlq.ai/news/cursor-says-hackers-used-a-key-exposed-at-fireworks-ai-to-plant-a-malicious-claude-code-extension-in-its-marketplace/
- https://dev.to/tin_thnhbnh_6d6c9102d/cursors-security-incident-explained-a-leaked-vendor-key-a-poisoned-extension-and-5000-users-47h4